Enable management of user identities in GUI
Hi Team,
following up on our Slack discussion.
Currently we have admin users that initially logged into a realm using local credentials and then using Keycloak OIDC. We want to disable local login for these users and keep only OIDC working + one local admin in the realm in case OIDC breaks.
Currently there’s no way to diassociate user identity (like OIDC or local login) from particular user.
Would it be possible to implement GUI similar to how Gitlab operates where user exists as one record but can be associated with multiple identities (like LDAP, OIDC, local login etc). If this existed, we would be able to “delete” the local identity from the user and keep only the OIDC identity if that makes sense.
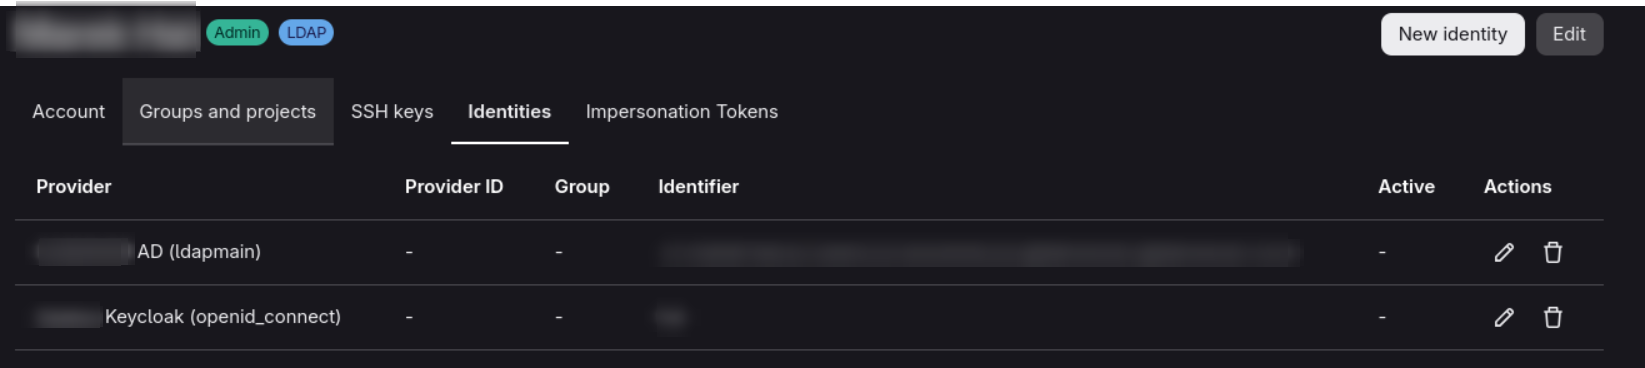
Thank you very much!
Status: Planned
Log in to comment and vote
No comments yet
Be the first to share your thoughts.